Real-time click alerts
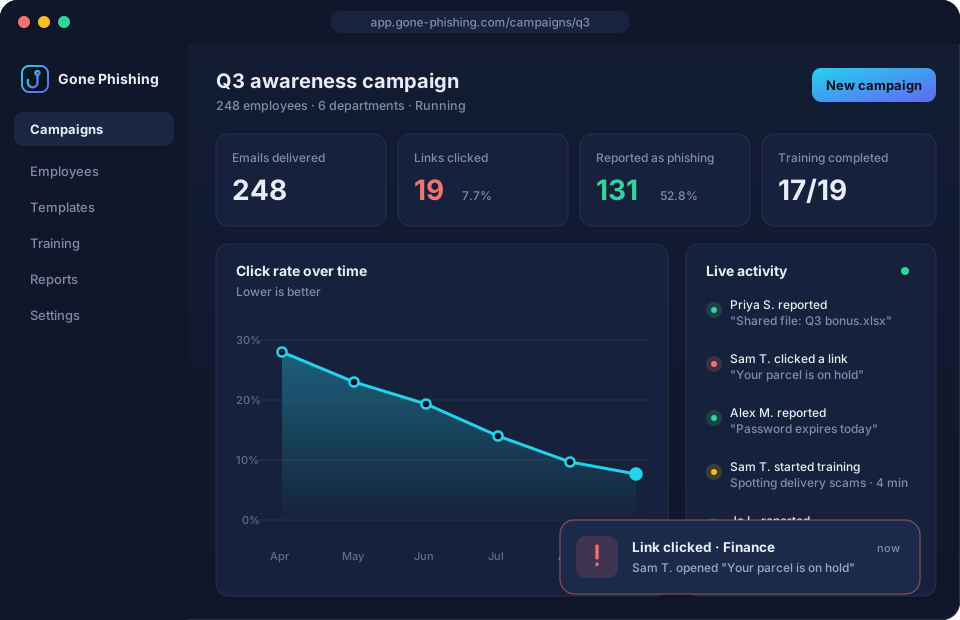
Get notified in the portal, by email or in Slack and Teams the moment a simulated link is clicked.
Now taking early access sign-ups
Gone Phishing sends realistic, targeted phishing simulations to your employees, alerts you the moment someone clicks, and turns every slip into a three-minute lesson.
Why it matters
Year after year, Verizon's Data Breach Investigations Report finds that the human element is involved in the majority of breaches. Phishing is how most attackers get in. The fix isn't more slide decks. It's practice.
Credential theft, invoice fraud and ransomware usually start with a single convincing email.
People learn to spot phishing by seeing it in their own inbox, not by signing a PDF once a year.
Track click and report rates by team over time, and show the board real progress.
How it works
Verify your domain, then import employees from Microsoft 365, Google Workspace or a CSV. Group them by department, location or role.
Pick from realistic templates (fake invoices, parcel notices, password resets, shared files) or write your own. Schedule sends over days so no one tips off the office.
See every open, click and report in real time. Anyone who clicks lands on a friendly page explaining the red flags they missed, plus a short follow-up lesson.
Features
Get notified in the portal, by email or in Slack and Teams the moment a simulated link is clicked.
Send finance a fake invoice and IT a fake MFA prompt. Test the threats each team actually faces.
Templates modelled on real-world attacks, refreshed regularly, with local Australian and international variants.
Reward the behaviour you want. Track who reports suspicious emails, not just who clicks.
Anyone who clicks gets a two-to-four minute lesson tied to the exact email they fell for.
Trends by team, repeat clickers, and training completion, exportable as PDF or CSV for audits.
The portal
Every simulated link is unique to the person who received it. When it's clicked, the event lands in your portal instantly, with who, which email, which department, and when.
Sam T. · Finance
Opened "Your parcel is on hold" from the Q3 awareness campaign.
Built for audits and insurers
Security awareness training is expected by the major frameworks and asked about on most cyber insurance forms. Gone Phishing gives you the records to prove it.
Who it's for
Run a proper awareness program without a dedicated security team. Set it once and let campaigns run monthly.
Measure human risk alongside your technical controls, and find the teams that need help most.
Manage campaigns for multiple clients from one login, with reports branded as your own.
FAQ
A phishing simulation is a safe, fake phishing email sent to your own employees. Nothing harmful happens when someone clicks. Instead, you learn who is at risk, and the employee gets a short lesson on the warning signs they missed.
Yes, when your organisation authorises it. Gone Phishing only sends to domains you have verified you own, and simulations never collect real passwords or personal data. We recommend telling staff that awareness testing is part of your security program.
Setup includes step-by-step allowlisting guides for Microsoft 365 and Google Workspace, so simulations reach inboxes the same way a real attack would.
Security awareness training is expected by frameworks such as ISO 27001, SOC 2, and the ACSC Essential Eight, and is often asked about by cyber insurers. Gone Phishing produces exportable reports that show testing frequency, results, and training completion.
Gone Phishing is in early access. Join the list and we will contact you directly. Founding customers get discounted pricing locked in and direct input into the roadmap.
Early access
We're onboarding a small group of organisations first. Tell us a little about your team and we'll reach out personally, usually within one business day.
Prefer email? hello@gone-phishing.com